Read the codebase like a proofreader reads a page.

vulnascan audits a codebase for vulnerable code and dependencies — each returned as errata: file, line, severity, fix.


Three flavours, one engine
Desktop app

A double-click installer for macOS, Windows and Linux. No terminal.

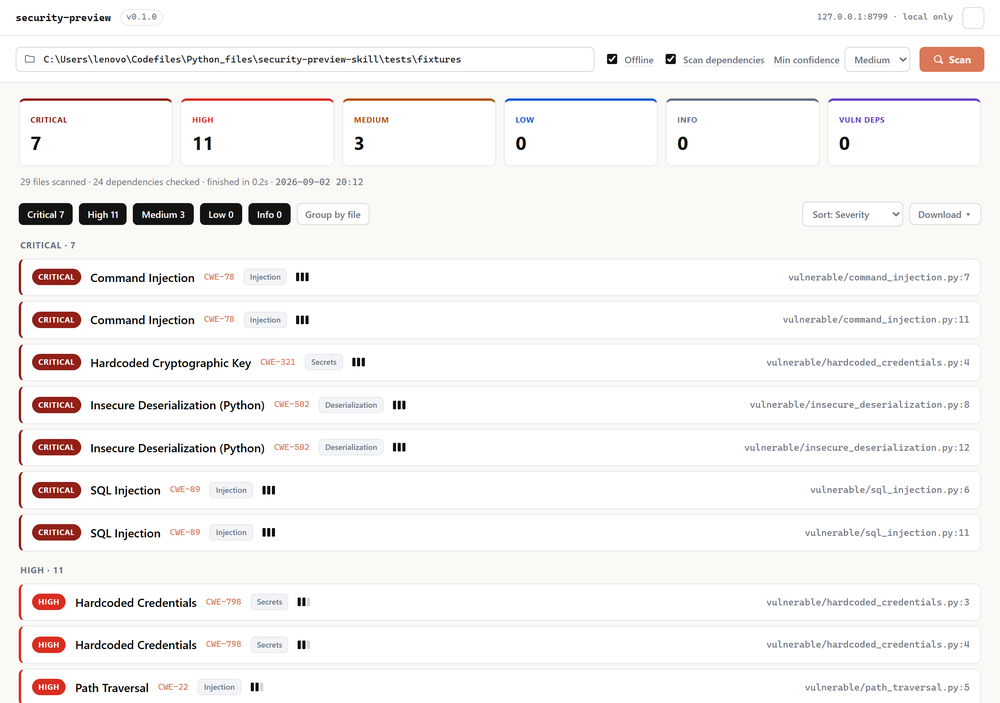
The vulnascan desktop app showing a completed scan, findings grouped by severity with counts in the margin.

CLI tool

Install from the repo, then scan any directory from the shell.

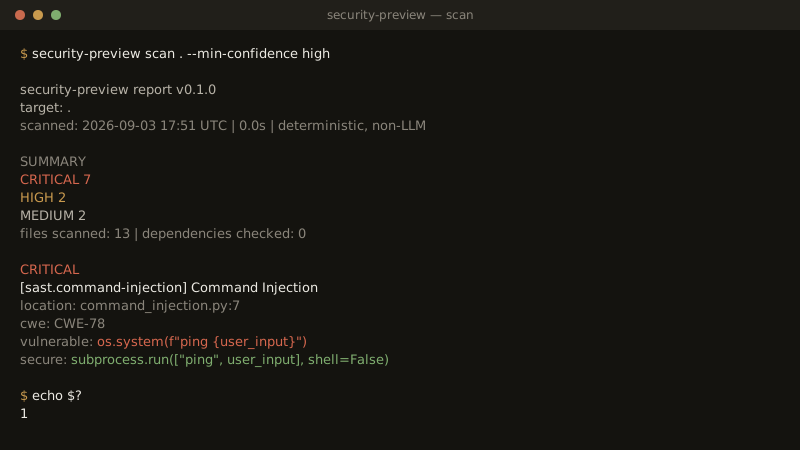
A terminal running security-preview scan: a severity summary, a command-injection finding at command_injection.py:7, and exit code 1.
security-preview scan . Install

Coding-agent skill

Add SKILL.md to Claude Code or Cursor, then just ask.

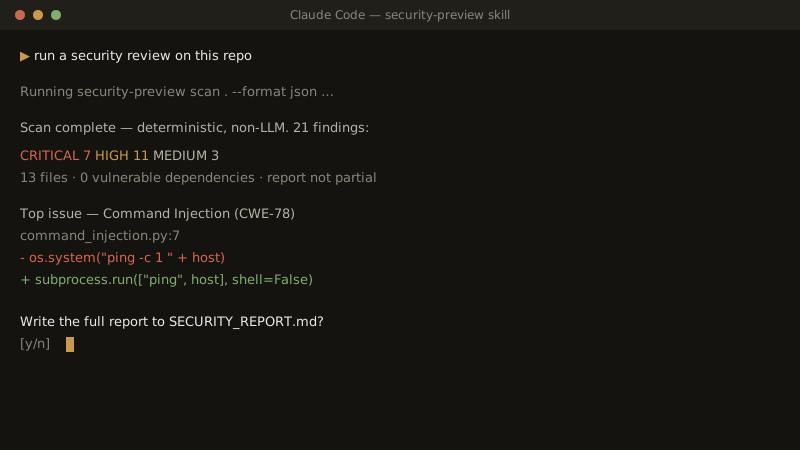
A Claude Code session running the security-preview skill: 21 findings summarised, and a proposed subprocess.run fix for a command-injection line.
/security-preview Set up